Cybersecurity · Artificial Intelligence · Tech

Engineering digital immunity for the modern enterprise

NivX Machines defends your business with AI-driven threat detection, zero-trust architecture, and real-time intelligence — turning raw signal into decisive defense.

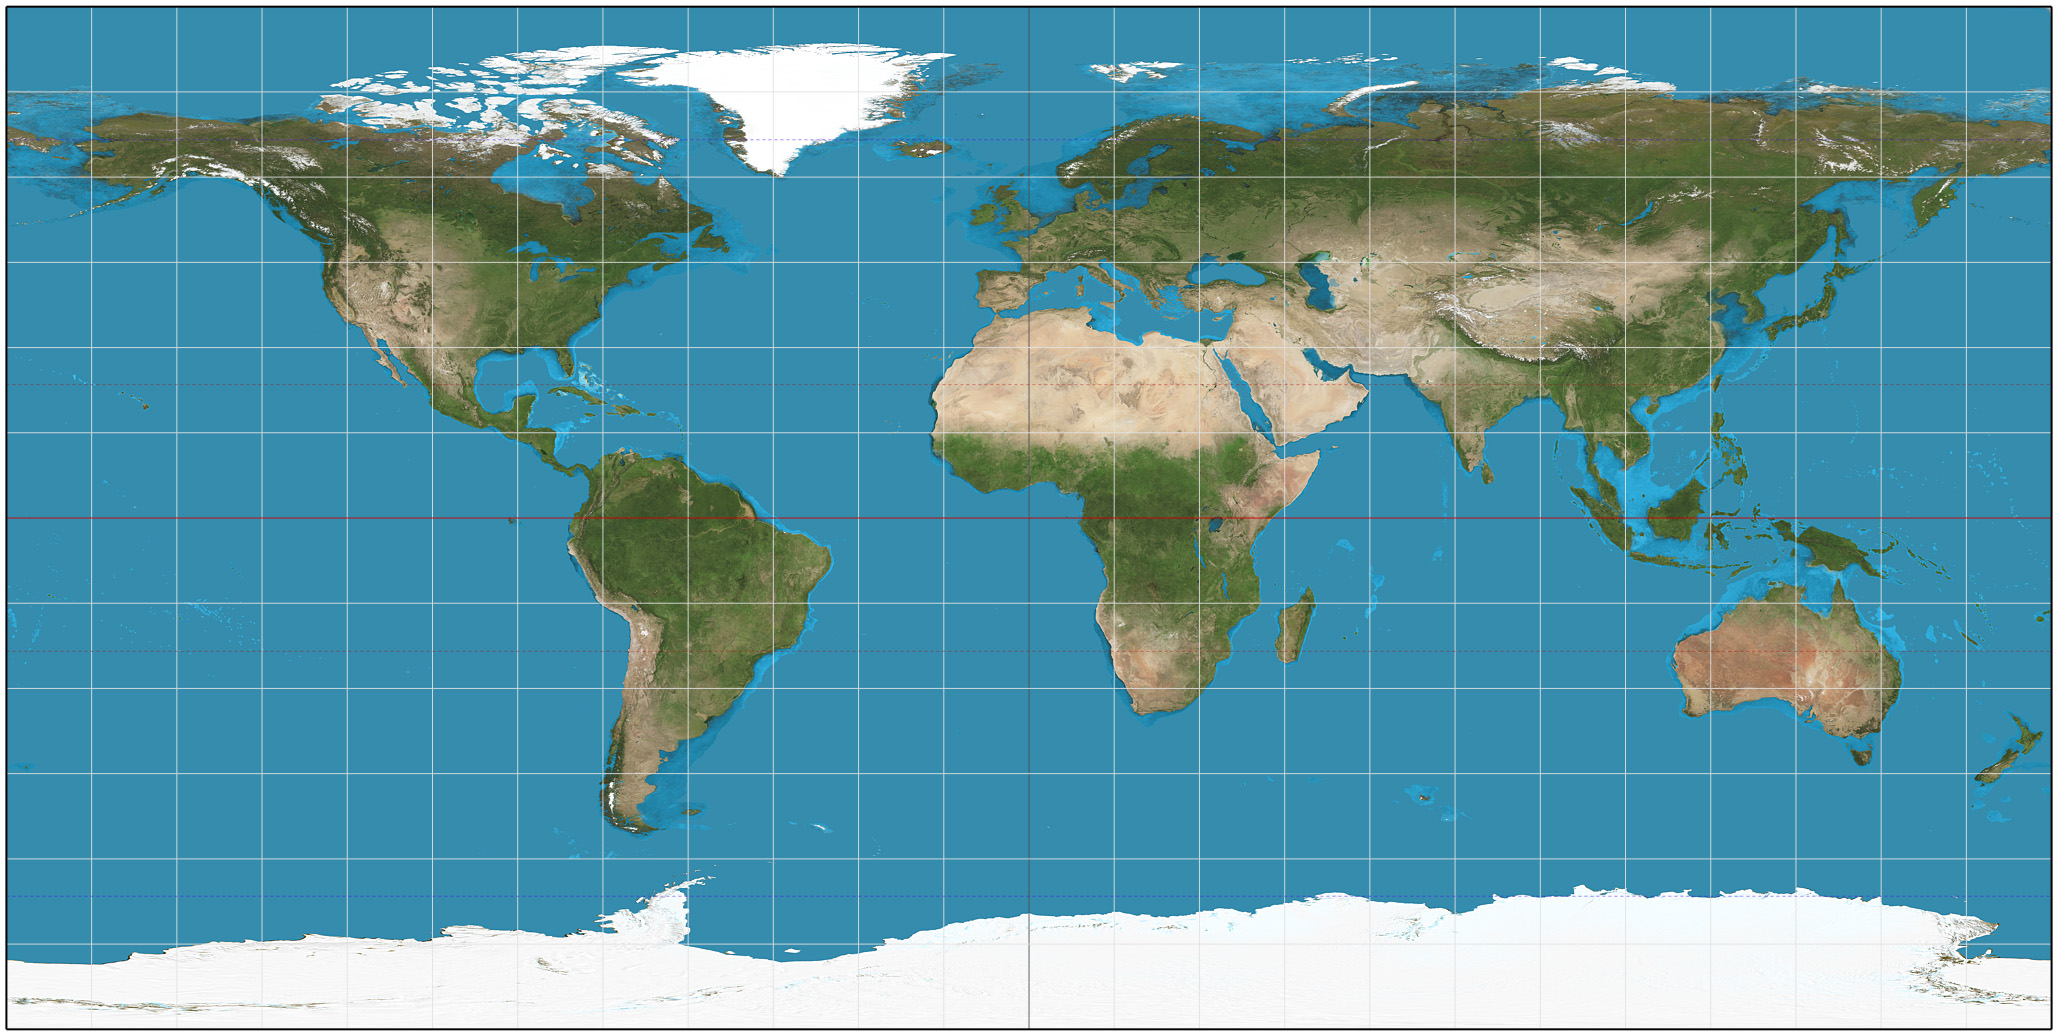
Global threat activity map
Live incident
Croatia
Barracuda · Ministarstvo poljoprivrede, šumarstva i ribarstva
Refreshed 8s ago
KEV tracked
1,739
Recent incidents
100
Victims 24h
12
About Us

Defense is a discipline, not a product

NivX Machines is a cybersecurity, AI and technology firm helping enterprises build resilient, intelligent defenses. Three principles guide everything we build.

01

Assume breach

We architect from the premise that adversaries are already inside — zero-trust segmentation and least-privilege access contain the blast radius.

02

Weaponize intelligence

Our AI models ingest telemetry at machine speed, correlating signals across endpoints, identity and network to surface what humans miss.

03

Respond at machine speed

Automated playbooks isolate, remediate and recover — collapsing dwell time from weeks to minutes.

24/7
SOC monitoring
<15min
Mean response time
99.9%
Uptime SLA
500+
Threats neutralized / day
Live · Real-Time Threat Landscape

The threat landscape, right now

Refreshed 0s ago· last cins_army sync 2m ago

Source: CISA Known Exploited Vulnerabilities
0
Exploited CVEs tracked
0
Ransomware-linked CVEs
0
New CVEs added (7d)
0
Curated IOCs
Live activity12 ransomware victims disclosed in last 24h79552 critical IOCs in curated DBMost recent: Barracuda · Ministarstvo poljoprivrede, šumarstva i ribarstva
Latest exploited vulnerabilities
50 of 50 LIVE
CVE-2015-5477
ISC BIND Data Processing Errors Vulnerability
ISC · BIND
2026-10-08
CVE-2016-3081
Apache Struts Command Injection Vulnerability
Apache · Struts
2026-10-08
CVE-2023-22894
Strapi Cleartext Storage of Sensitive Information Vulnerability
Strapi · Strapi
2026-10-08
CVE-2021-3199
ONLYOFFICE Docs Server Path Traversal Vulnerability
ONLYOFFICE · Docs
2026-10-08
CVE-2015-3306
ProFTPD Improper Access Control Vulnerability
ProFTPD · ProFTPD
2026-10-08
CVE-2026-88779
Citrix NetScaler Improper Restriction of Operations within the Bounds of a Memory Buffer Vulnerability
Citrix · NetScaler
2026-10-04
CVE-2026-102490
Zammad GmbH Zammad Improper Privilege Management Vulnerability
Zammad GmbH · Zammad
2026-10-02
CVE-2026-102489
Zammad GmbH Zammad Session Fixation Vulnerability
Zammad GmbH · Zammad
2026-10-02
CVE-2026-104286
Fortinet FortiMail Path Traversal Vulnerability
Fortinet · FortiMail
2026-10-01
CVE-2026-76504
Cisco Catalyst SD-WAN Manager Hex Encoding Vulnerability
Cisco · Catalyst SD-WAN Manager
2026-09-30
CVE-2026-86950
Apple Multiple Products Out-of-Bounds Write Vulnerability
Apple · Multiple Products
2026-09-29
CVE-2026-88772
Citrix NetScaler Improper Restriction of Operations within the Bounds of a Memory Buffer Vulnerability
Citrix · NetScaler
2026-09-27
CVE-2026-88771
Citrix NetScaler Improper Input Validation Vulnerability
Citrix · NetScaler
2026-09-27
CVE-2026-67279
Mikrotik RouterOS Improper Enforcement of Behavioral Workflow Vulnerability
MikroTik · RouterOS
2026-09-25
CVE-2026-65660
Microsoft SharePoint Code Injection Vulnerability
Microsoft · SharePoint
2026-09-25
CVE-2026-87902
WordPress Core Remote File Inclusion Vulnerability
WordPress · Core
2026-09-25
CVE-2026-5430
WSO2 Multiple Products Path Traversal Vulnerability
WSO2 · Multiple Products
2026-09-24
CVE-2026-71362
Adobe Commerce and Magento Incorrect Authorization Vulnerability
Adobe · Commerce and Magento
2026-09-24
CVE-2026-93952
Arista VeloCloud Orchestrator Improper Input Validation Vulnerability
Arista · VeloCloud Orchestrator
2026-09-22
CVE-2026-94127
F5 BIG-IP APM Heap-based Buffer Overflow Vulnerability
F5 · BIG-IP APM
2026-09-22
CVE-2026-93616
Check Point Multiple Products Path Traversal Vulnerability
Check Point · Multiple Products
2026-09-22
CVE-2026-85102
Check Point Multiple Products Improper Certificate Validation Vulnerability
Check Point · Multiple Products
2026-09-22
CVE-2026-7273
Zyxel GS1900 Series Switches Stack-Based Buffer Overflow Vulnerability
Zyxel · GS1900 Series Switches
2026-09-21
CVE-2025-39964
Linux Kernel Race Condition Vulnerability
Linux · Kernel
2026-09-18
CVE-2026-53266
Linux Kernel Out-of-Bounds Write Vulnerability
Linux · Kernel
2026-09-18
CVE-2025-39682
Linux Kernel Improper Check for Unusual or Exceptional Conditions Vulnerability
Linux · Kernel
2026-09-18
CVE-2026-58704
Google Pixel Improper Authorization Vulnerability
Google · Pixel
2026-09-16
CVE-2026-76460
Cisco Identity Services Engine Incorrect Use of Privileged APIs Vulnerability
Cisco · Identity Services Engine
2026-09-16
CVE-2026-87886
Acronis Backup Incorrect Default Permissions Vulnerability
Acronis · Backup
2026-09-16
CVE-2026-76461
Cisco Secure Email Gateway SQL Injection Vulnerability
Cisco · Secure Email Gateway
2026-09-14
CVE-2026-84869
ConnectWise ScreenConnect Improper Privilege Management and Missing Authorization Vulnerability
ConnectWise · ScreenConnect
2026-09-11
CVE-2026-42016
JFrog Artifactory Incorrect Authorization Vulnerability
JFrog · Artifactory
2026-09-11
CVE-2026-42018
JFrog Artifactory Improper Authentication Vulnerability
JFrog · Artifactory
2026-09-11
CVE-2026-85706
GitLab Community Edition and Enterprise Edition Path Traversal Vulnerability
GitLab · Community Edition and Enterprise Edition
2026-09-11
CVE-2026-86060
MikroTik RouterOS Improper Neutralization of Argument Delimiters in a Command Vulnerability
MikroTik · RouterOS
2026-09-10
CVE-2026-67277
MikroTik RouterOS Missing Authentication for Critical Function Vulnerability
MikroTik · RouterOS
2026-09-10
CVE-2026-19490
Citrix NetScaler Authentication Bypass Using an Alternate Path or Channel Vulnerability
Citrix · NetScaler
2026-09-09
CVE-2025-25249
Fortinet Multiple Products Heap-based Buffer Overflow Vulnerability
Fortinet · Multiple Products
2026-09-09
CVE-2026-87491
Google Chromium V8 Out of Bounds Write Vulnerability
Google · Chromium V8
2026-09-09
CVE-2026-20079
Cisco Firewall Management Center Authentication Bypass Using an Alternate Path or Channel Vulnerability
Cisco · Secure Firewall Management Center (FMC) and Security Cloud Control (SCC) Firewall Management
2026-09-09
CVE-2026-75650
Adobe Commerce and Magento Improper Neutralization of Special Elements Used in a Template Engine Vulnerability
Adobe · Commerce and Magento
2026-09-08
CVE-2026-81963
Microsoft Windows Link Following Vulnerability
Microsoft · Windows
2026-09-08
CVE-2026-86218
N-able N-central Static Code Injection Vulnerability
N-able · N-central
2026-09-08
CVE-2026-85880
Microsoft Windows Heap-Based Buffer Overflow Vulnerability
Microsoft · Windows
2026-09-08
CVE-2026-85046
Google Chromium V8 Type Confusion Vulnerability
Google · Chromium V8
2026-09-04
CVE-2026-59822
BerriAI LiteLLM Improper Authentication Vulnerability
BerriAI · LiteLLM
2026-09-02
CVE-2026-48710
Kludex Starlette HTTP Request/Response Smuggling Vulnerability
Kludex · Starlette
2026-09-02
CVE-2026-49869
Kestra OSS OS Command Injection Vulnerability
Kestra · Kestra OSS
2026-09-02
CVE-2026-82329
JFrog Artifactory Improper Authentication Vulnerability
JFrog · Artifactory
2026-09-02
CVE-2026-9586
Sangoma Switchvox SQL Injection Vulnerability
Sangoma · Switchvox
2026-09-02
Internal Advisories· 6
Supersede CISA rows for the same CVE
CVE-2025-2492
ASUS AiCloud Router Improper Access Control
ASUS · AiCloud Routers · added by admin@nivxmachines.com
Manual
CVE-2026-40138
BeyondTrust Remote Support and Privileged Remote Access Authentication Bypass
BeyondTrust · Remote Support (RS) and Privileged Remote Access (PRA) · added by admin@nivxmachines.com
Manual
CVE-2026-43499
GhostLock
Linux · Kernel · added by admin@nivxmachines.com
Manual
CVE-2026-46242
Bad Epoll
Linux · Kernel · added by admin@nivxmachines.com
Manual
CVE-2026-44747
SAP NetWeaver Application Server ABAP Memory Corruption
SAP · NetWeaver Application Server ABAP · added by admin@nivxmachines.com
Manual
CVE-2026-47865
VMware Avi Load Balancer Authentication Bypass Vulnerability
VMware · Avi Load Balancer · added by admin@nivxmachines.com
Manual
Live · Global Attack Telemetry

Who’s attacking the internet right now

Aggregated real-time attack telemetry from the world’s largest public honeypot networks and community threat-intel feeds — refreshed every minute.

Top attacker IPs

  1. #113.94.254.200319,739reports
  2. #2194.224.249.214309,508reports
  3. #352.157.207.201194,780reports
  4. #489.248.163.10996,279reports
  5. #5143.244.186.3592,007reports
  6. #618.116.198.19159,907reports
  7. #7152.89.198.16341,378reports
  8. #8152.89.198.10341,346reports
  9. #9152.89.198.18741,332reports
  10. #10185.122.204.7141,221reports
  11. #11176.113.115.10441,164reports
  12. #1291.240.118.5941,148reports
  13. #1362.204.41.20541,094reports
  14. #14152.89.198.6140,959reports
  15. #1562.233.50.24540,869reports

Active botnet C2s

C21.161.100.47
C21.161.104.149
C21.161.104.31
C21.161.116.40
C21.161.118.53
C21.161.121.58
C21.161.122.145
C21.161.123.180
C21.161.123.53
C21.161.124.241
C21.161.126.13
C21.161.126.64
C21.161.66.82
C21.161.67.235
C21.161.71.109
C21.161.72.70
C21.161.75.18
C21.161.79.116
C21.161.80.70
C21.161.80.99
C21.161.81.21
C21.161.88.84
C21.161.97.158
C21.221.179.74
C21.234.2.232
Attack telemetry aggregated from public feeds: SANS DShield honeypot network, URLhaus, and Feodo Tracker — updated 9:47:31 AM. No proprietary vendor data; all sources link back to origin.
Services

Full-spectrum defense

End-to-end cybersecurity, AI and technology services engineered for enterprise resilience.

Managed Detection & Response

24/7 SOC monitoring with AI-triaged alerts and human-led threat hunting.

Learn more

AI Security Engineering

Custom ML models for anomaly detection, fraud, and behavioral analytics.

Learn more

Zero-Trust Architecture

Identity-first segmentation and least-privilege access design.

Learn more

Offensive Security

Red teaming, penetration testing, and adversary emulation.

Learn more

Cloud & Infra Hardening

CSPM, container security, and secure DevOps pipelines.

Learn more

Incident Response & Forensics

Rapid containment, root-cause forensics, and recovery orchestration.

Learn more